SOC 2 Type 2 : how each Common Criterion is tested in a Secure SDLC
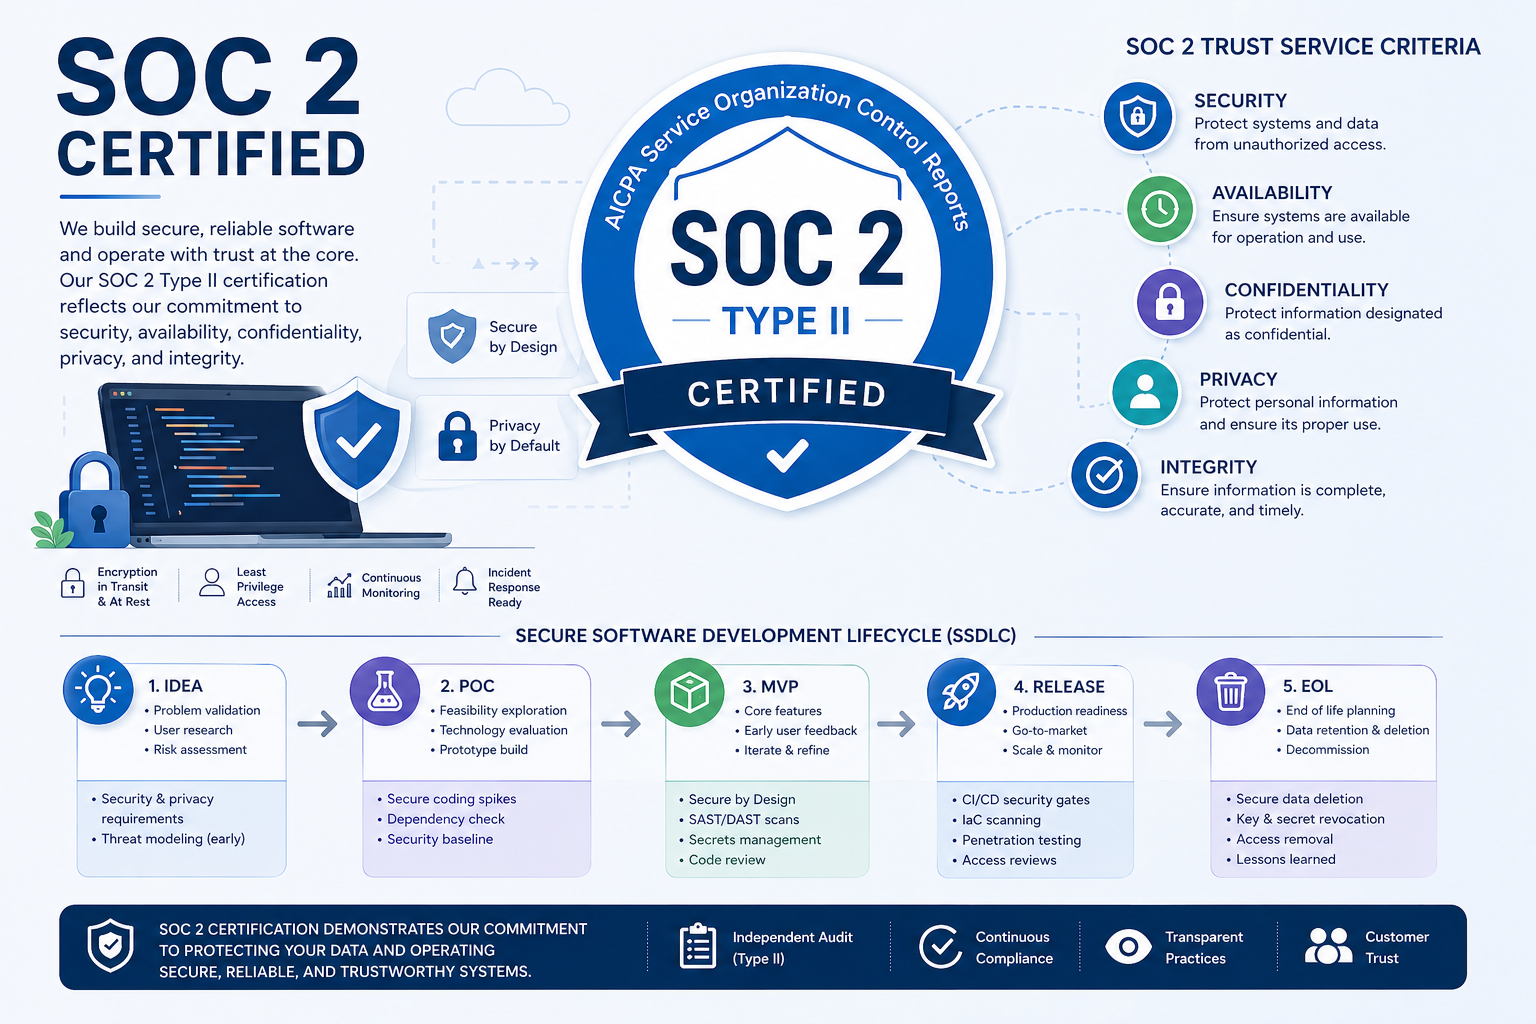
In April I published a mapping of the SOC 2 Type 2 Common Criteria to Secure SDLC requirements. That article answers the question “which criterion touches which SDLC phase”. This one answers the question that comes right after it in every readiness project: how does the auditor actually test each criterion, and what makes a […]
You must be logged in to post a comment.