Quick pick

SSDLC

SSDLC

18 posts
ISO 27001

ISO 27001

19 posts
TISAX

TISAX

9 posts
Security

Security

163 posts
General

ISO27001 and GDPR

We are talking about Article 32 of GDPR: https://gdpr-info.eu/art-32-gdpr/ It basically says that you should have some measures in place in order to protect customer data by reducing the risk of a customer data to be lost or stolen(through a data breach, through classical theft, losing drives, making information public unintentionally an so on).   […]
Phishing

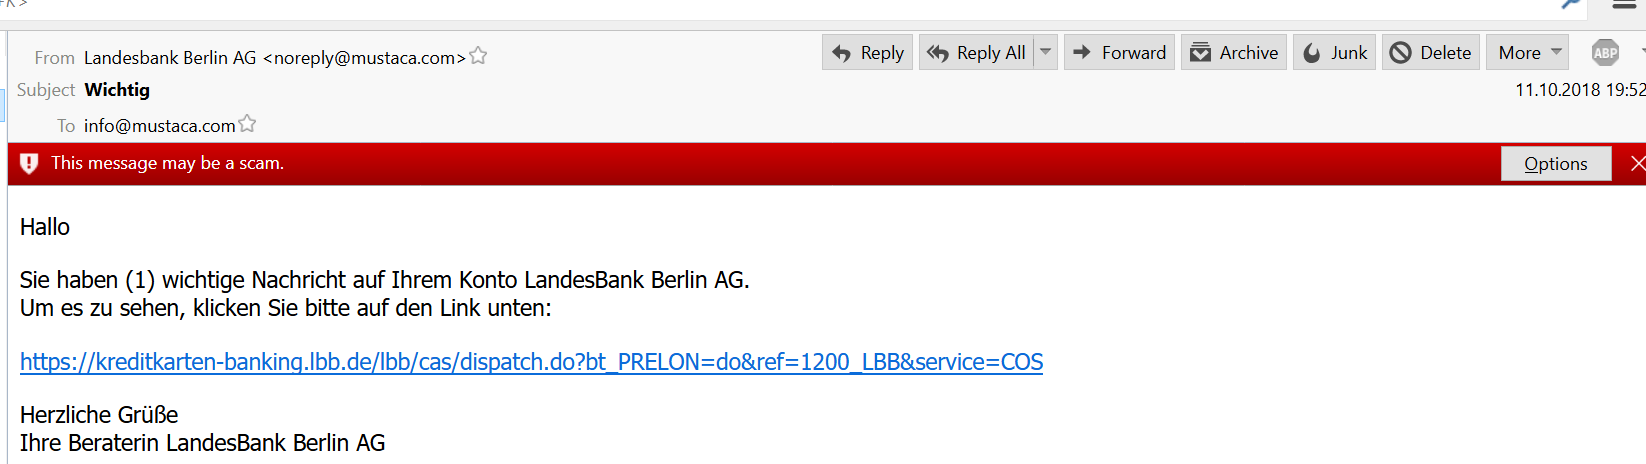
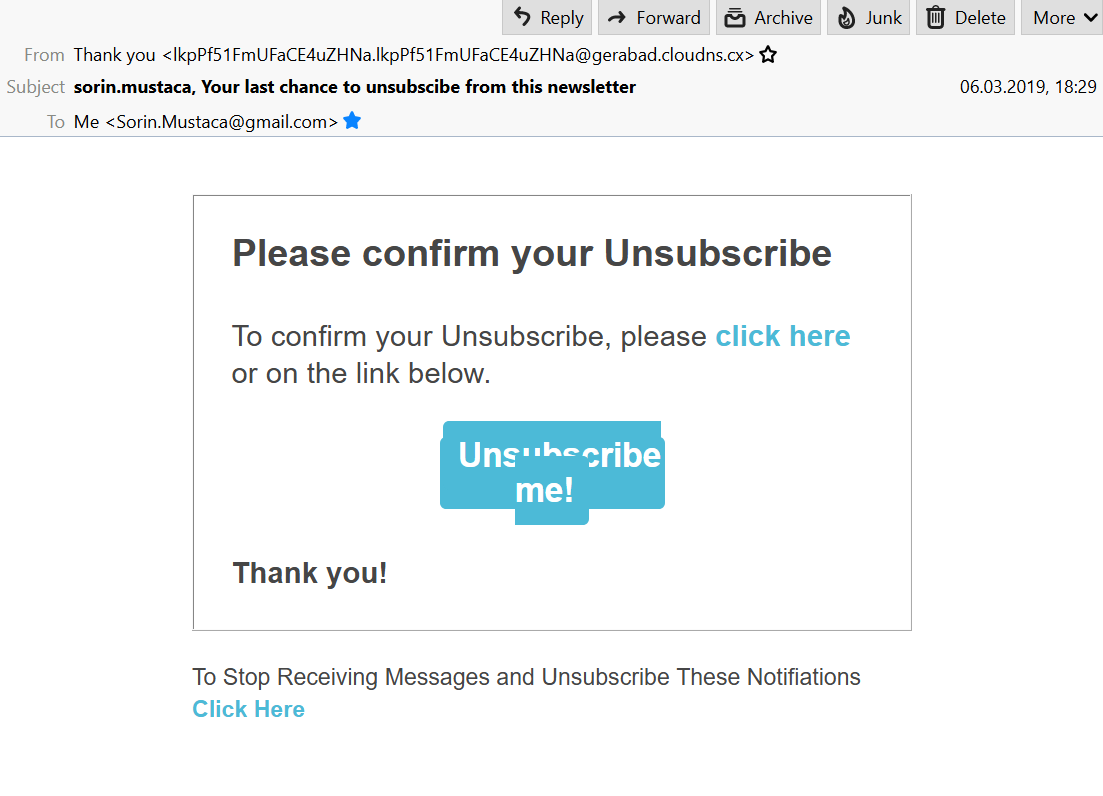
Targeted phishing for Amazon Credit Cards

This time, there is a phishing for Amazon Credit Cards, which are served by LBB Bank. The user is redirected twice to some URLs, which are reported as “DECEPTIVE” by Chrome. Unfortunately, the final pages were deleted, so I can’t take screenshots.   Hallo Sie haben (1) wichtige Nachricht auf Ihrem Konto LandesBank Berlin AG. […]

News Phishing Security

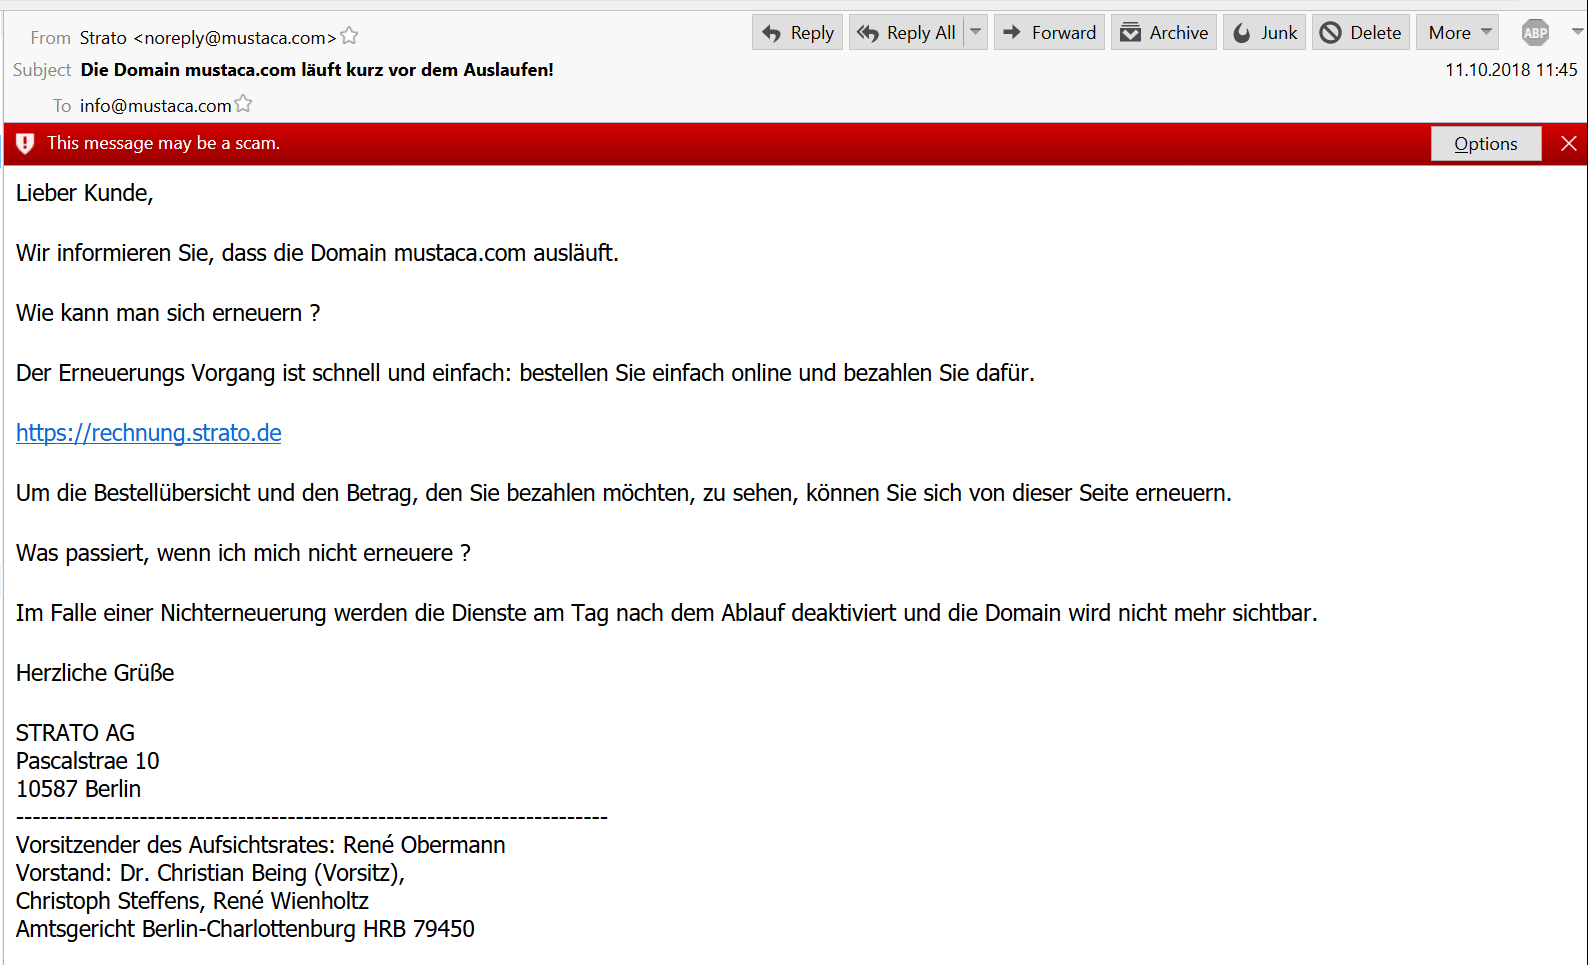
Targeted phishing on customers of Strato.de

My domain mustaca.com is hosted at Strato.de. I received several such emails, showing that somebody really scrapes the next for finding targets of various ISPs. Lieber Kunde, Wir informieren Sie, dass die Domain mustaca.com ausläuft. Wie kann man sich erneuern ? Der Erneuerungs Vorgang ist schnell und einfach: bestellen Sie einfach online und bezahlen Sie […]

(isc)2 News

SAFECODE.ORG: security fundamentals for developers

If you don’t know safecode.org, then stop reading this article and click here: https://safecode.org/about-safecode/ SAFECode – short for the Software Assurance Forum for Excellence in Code – spearheads a global, industry-wide effort to identify and promote best practices for developing and delivering more secure and reliable software, hardware and services. Here is a short film about […]